Stop the fake shop before your customers pay it.
Retailers are cloned to defraud their customers and phished for payment data and supplier payments. SafeToOpen helps you find the fakes wearing your name and protects your own people at the click.
Shopping fraud, in numbers
How SafeToOpen helps
Find the fakes wearing your name, and protect your own people at the click.
Lookalike domains and cloned checkouts
Brand Protection finds typosquats and cloned sites from the referral URLs your web server already logs, scores each one and alerts your team with the evidence.
Card data in the wrong place
Paste Guard redacts card numbers on paste, on the device, and flags personal data before it is sent to a website or AI tool.
Supplier invoices and payment requests
One click in Outlook or Gmail shows what doesn’t add up in a payment request, such as new bank details from a domain that is days old.
Customers who can tell
Scam Check can test your staff or your customers on real scam techniques, with your name and colours on the test.
Checked, not just claimed
Read more
Fake online stores & shopping scams
Too-good deals, cloned checkouts and fake stores: how to spot one before you enter your card.
Read it → ScamsBlack Friday & Cyber Monday scams: how to shop safely
Fake shops, cloned checkouts and deal texts spike every November. The checks that catch them before you pay.
Read it → Brand ProtectionBrand impersonation 101
Why scammers clone your brand, and how takedowns work.
Read it →Questions, answered
Your public web server already records the referral URL of every visit. When a half-built phishing page points at your real sign-in or checkout, its address appears in those logs. Brand Protection turns that stream into an alert, with the evidence your team needs.
Customers who use the free SafeToOpen extension are warned on fake pages that copy you. Scam Check can also test customers, with your name and colours on the test.
No. SafeToOpen never collects, stores or sells browsing data. It processes only the minimum needed to confirm a threat and deletes it after analysis.
For retailers
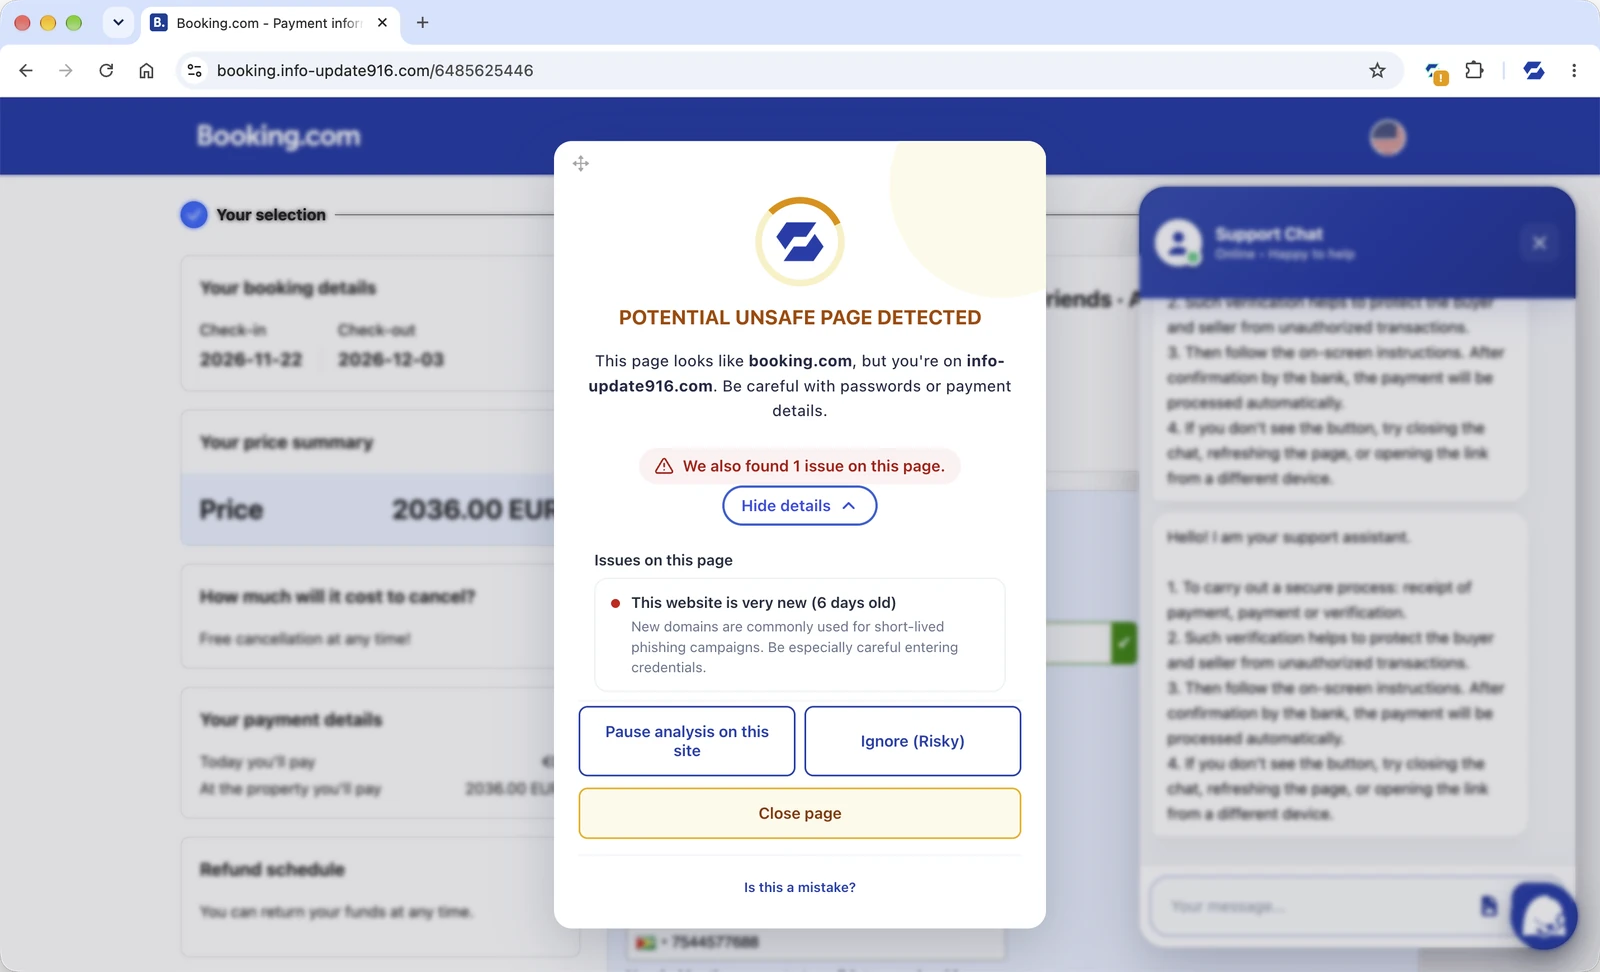
See it on a cloned checkout
Tell us a little about your business and we’ll show you Brand Protection and SafeToOpen in the browser.
- We reply by email to find a time that suits you.
- We only use your details to reply to your request.
- Prefer to start on your own? Start a free trial →