Protects the inbox
Protects the inbox
Verify any suspicious email in Outlook & Gmail in one click — trust scores, attachment & link checks, and Deeper Analysis for BEC and targeted attacks.
Now on the Google Workspace Marketplace
ExploreBrand-new phishing gets past email filters because nobody has seen it yet. SafeToOpen checks the page as it loads and blocks it before a password is entered.
Built for the sectors where phishing hits hardest — Healthcare · Universities · Government · Construction · Manufacturing · Professional services · Law firms · Insurance · Banking
Threats reach your organization through the inbox, the browser, and by impersonating your brand to your customers — and you can embed the same detection in your own systems. Enterprise and government teams get all four, powered by one real-time, zero-day engine — plus Scam Check to measure your people and LogLens to get the most out of your SIEM.
Protects the inbox
Protects the inbox
Verify any suspicious email in Outlook & Gmail in one click — trust scores, attachment & link checks, and Deeper Analysis for BEC and targeted attacks.
Now on the Google Workspace Marketplace
ExploreProtects the browser
Protects the browser
Catches never-before-seen phishing pages as they load — plus malware & malicious-site blocking, and guardrails that stop sensitive data being pasted out. Works on desktop and mobile alike, including Microsoft Edge on Android — installed and registered exactly as on desktop.
ExploreSecurity awareness test
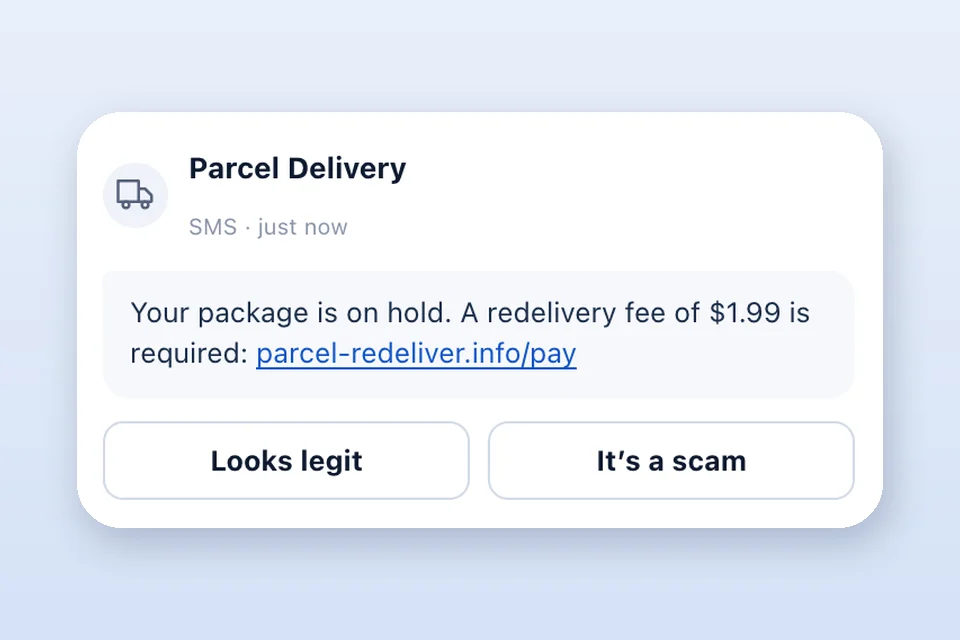
Security awareness test
A short, timed, branded test built from real scam techniques shows who would fall for a scam, scored per person across email, text, phone and QR. Nobody is tricked, and the first campaign is free.
ExploreGets more from your SIEM
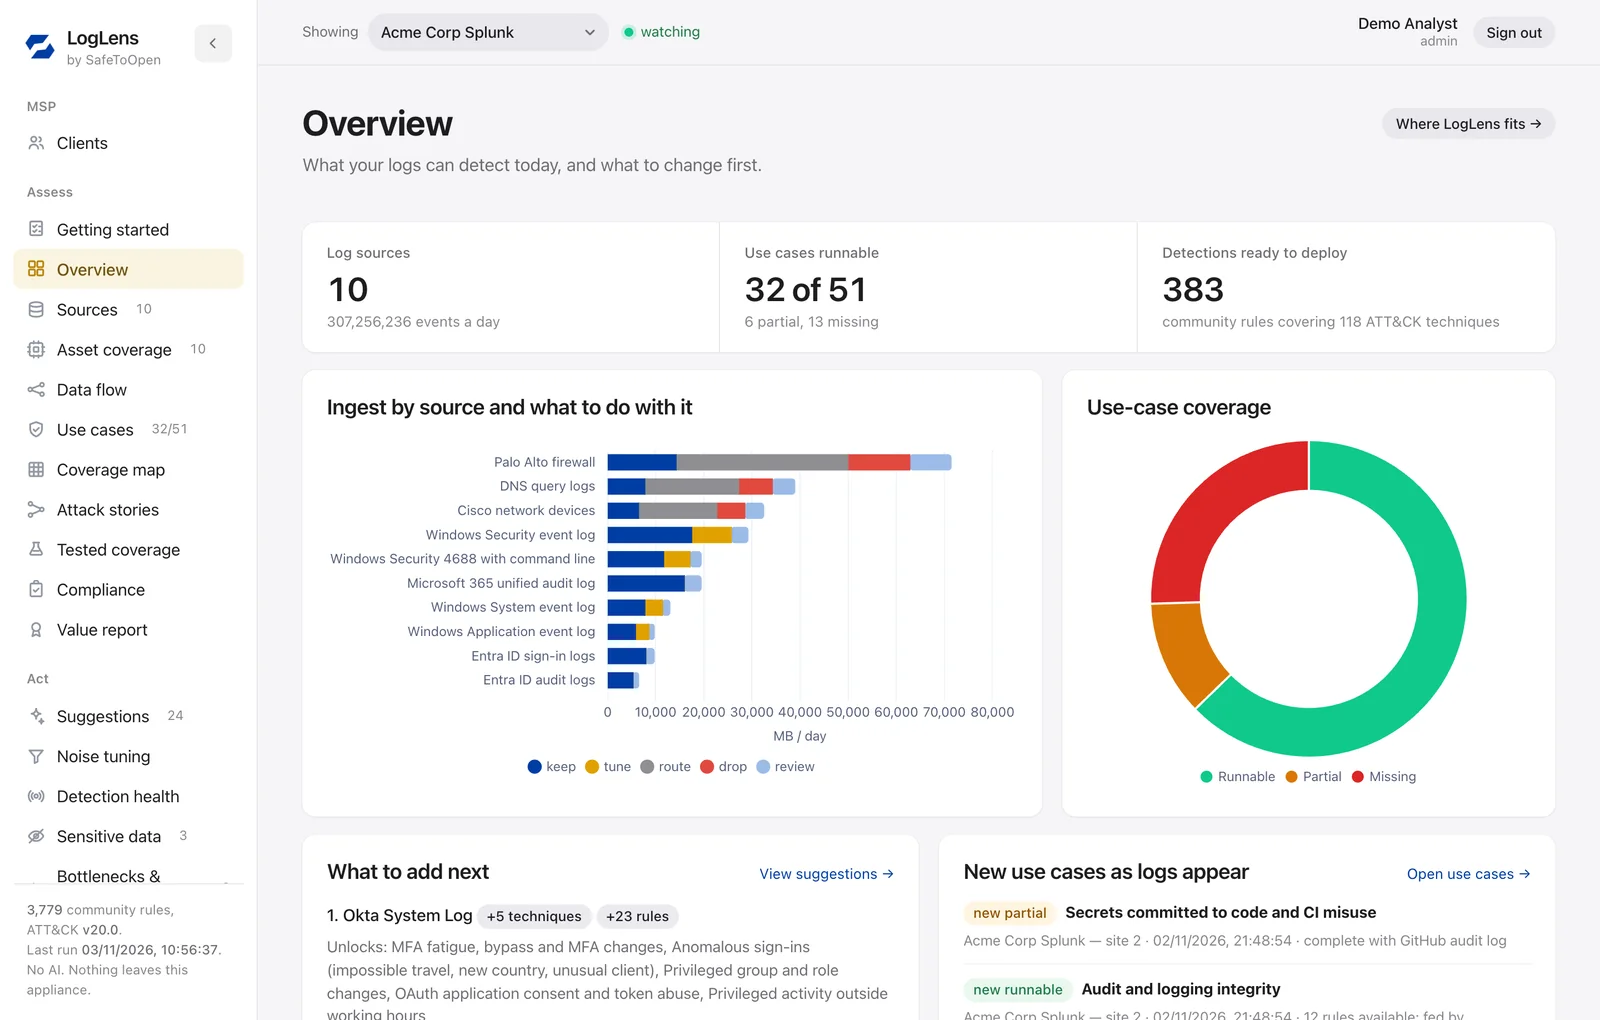
Gets more from your SIEM
Maps your SIEM’s logs to MITRE ATT&CK, shows the ingest no detection uses, and deploys reviewed detections to your SIEM and response playbooks to your SOAR. Uses no AI, and can run offline on-premises.
ExploreProtects your customers
Protects your customers
Detects sites and emails impersonating your brand and reports them — so scams aimed at your customers are flagged fast.
ExploreEmbeds in your systems
Embeds in your systems
Bring the same real-time detection engine into your own products, portals and automated security workflows.
ExploreThe four protection products share one engine and one console — deploy what you need, manage it together. Running a security team? Read the Browser Security capabilities & data-protection overview →. See plans →
Your stack can tell you what it blocked. It cannot tell you what your people would do with whatever gets through — and no software catches everything. Scam Check sends a short, timed, branded test built from real techniques seen between 2024 and 2026 and scores it person by person and team by team: the number you put in front of a board, and the baseline you re-measure against after a rollout or an incident.
ISO/IEC 27001:2022 certified and independently pen-tested. Security whitepaper, data-handling statement, AI transparency, sub-processor register and SLA are published in our Trust Center; the full review pack (SoA, pen-test summary, CAIQ) is available under NDA with one-business-day turnaround. Visit the Trust Center →
Three ways to see SafeToOpen work, before you talk to anyone.
Paste any link and get a verdict in seconds. No sign-up, and nothing opens on your device.
Run your first Scam Check campaign free and get a real results dashboard for your team.
Roll it out to your team with no credit card, and cancel any time.
SafeToOpen catches zero-day threats in the two places they reach your people. Pick a layer to see how.
A zero-day phishing email passes every reputation-based control — gateway, training, web filter — because none of them have seen it before. SafeToOpen scans the page live in the browser and blocks it where it counts.
The moment SafeToOpen blocks a page, it doesn't stop at the browser. The threat is turned into a signal that protects the user, your security team, and the wider community.
When a suspicious email lands, SafeToOpen Email Security checks the headers, links, QR codes, attachments and sender — catching never-before-seen phishing — then tells the user whether it's safe.
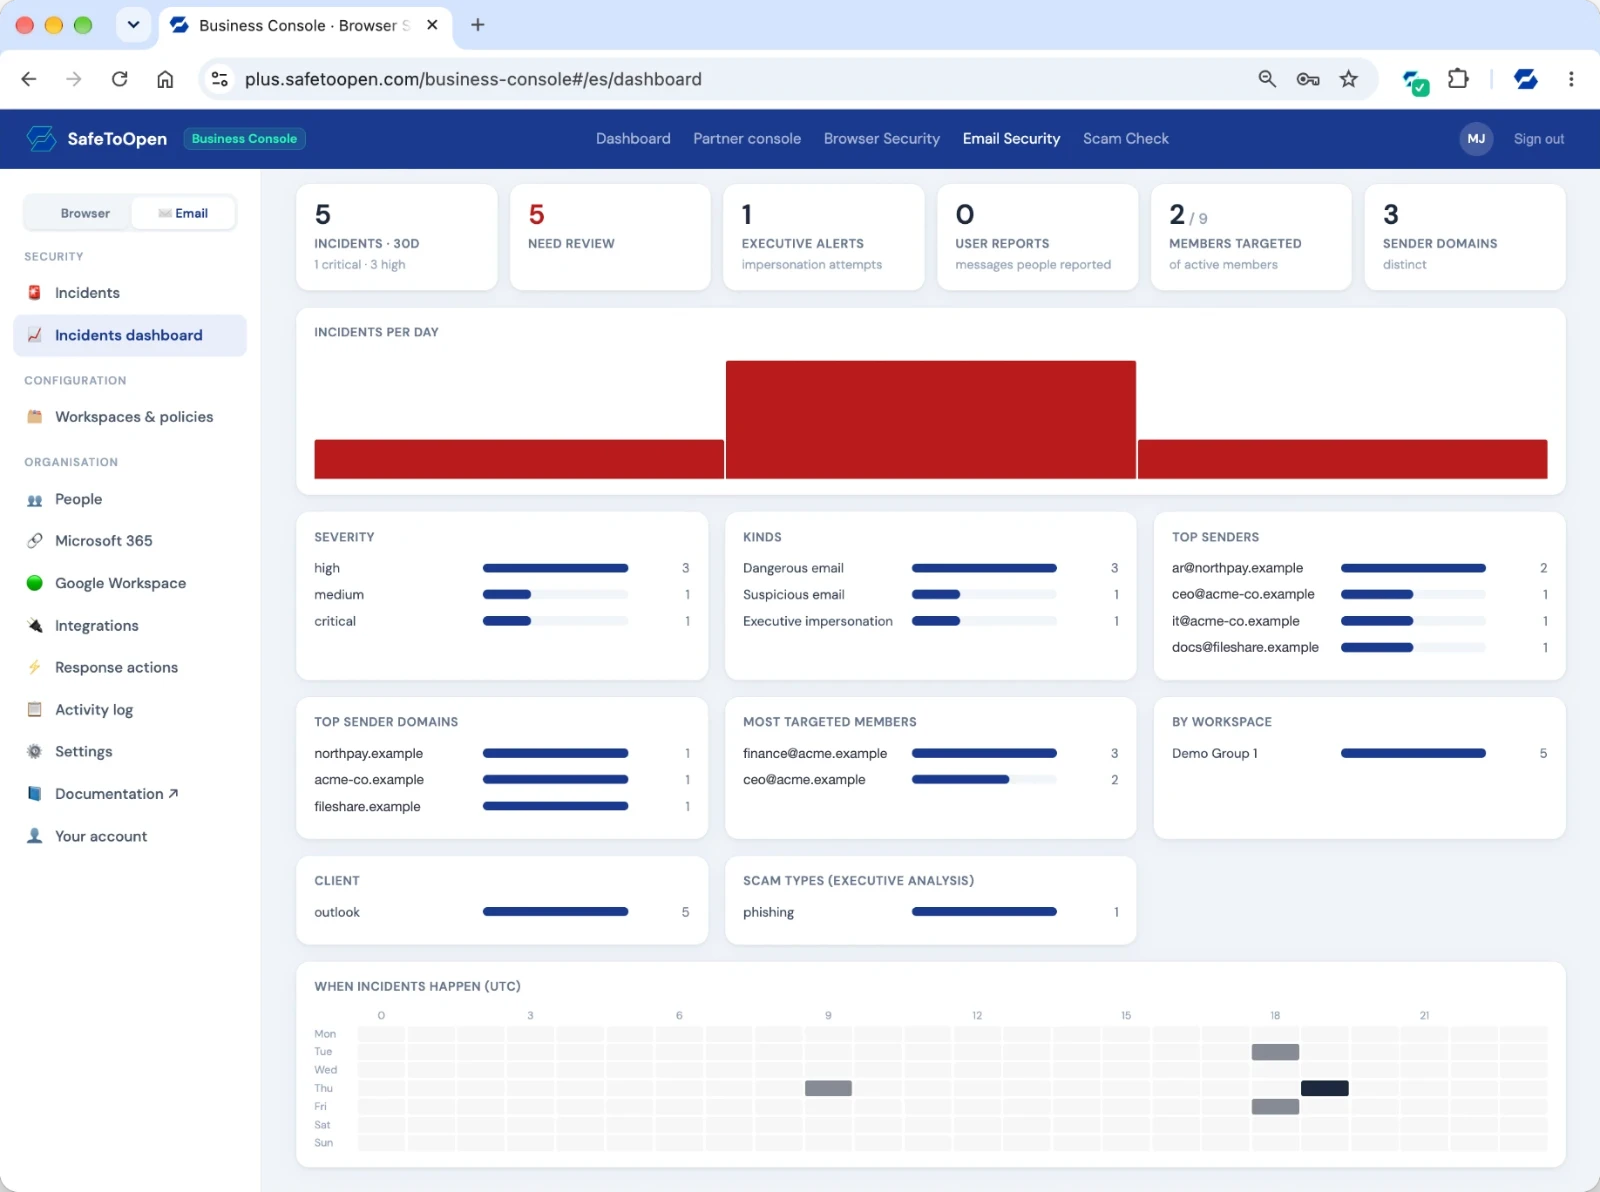
See incidents, the people being targeted and the senders behind them, across every mailbox.
Shown with test data.
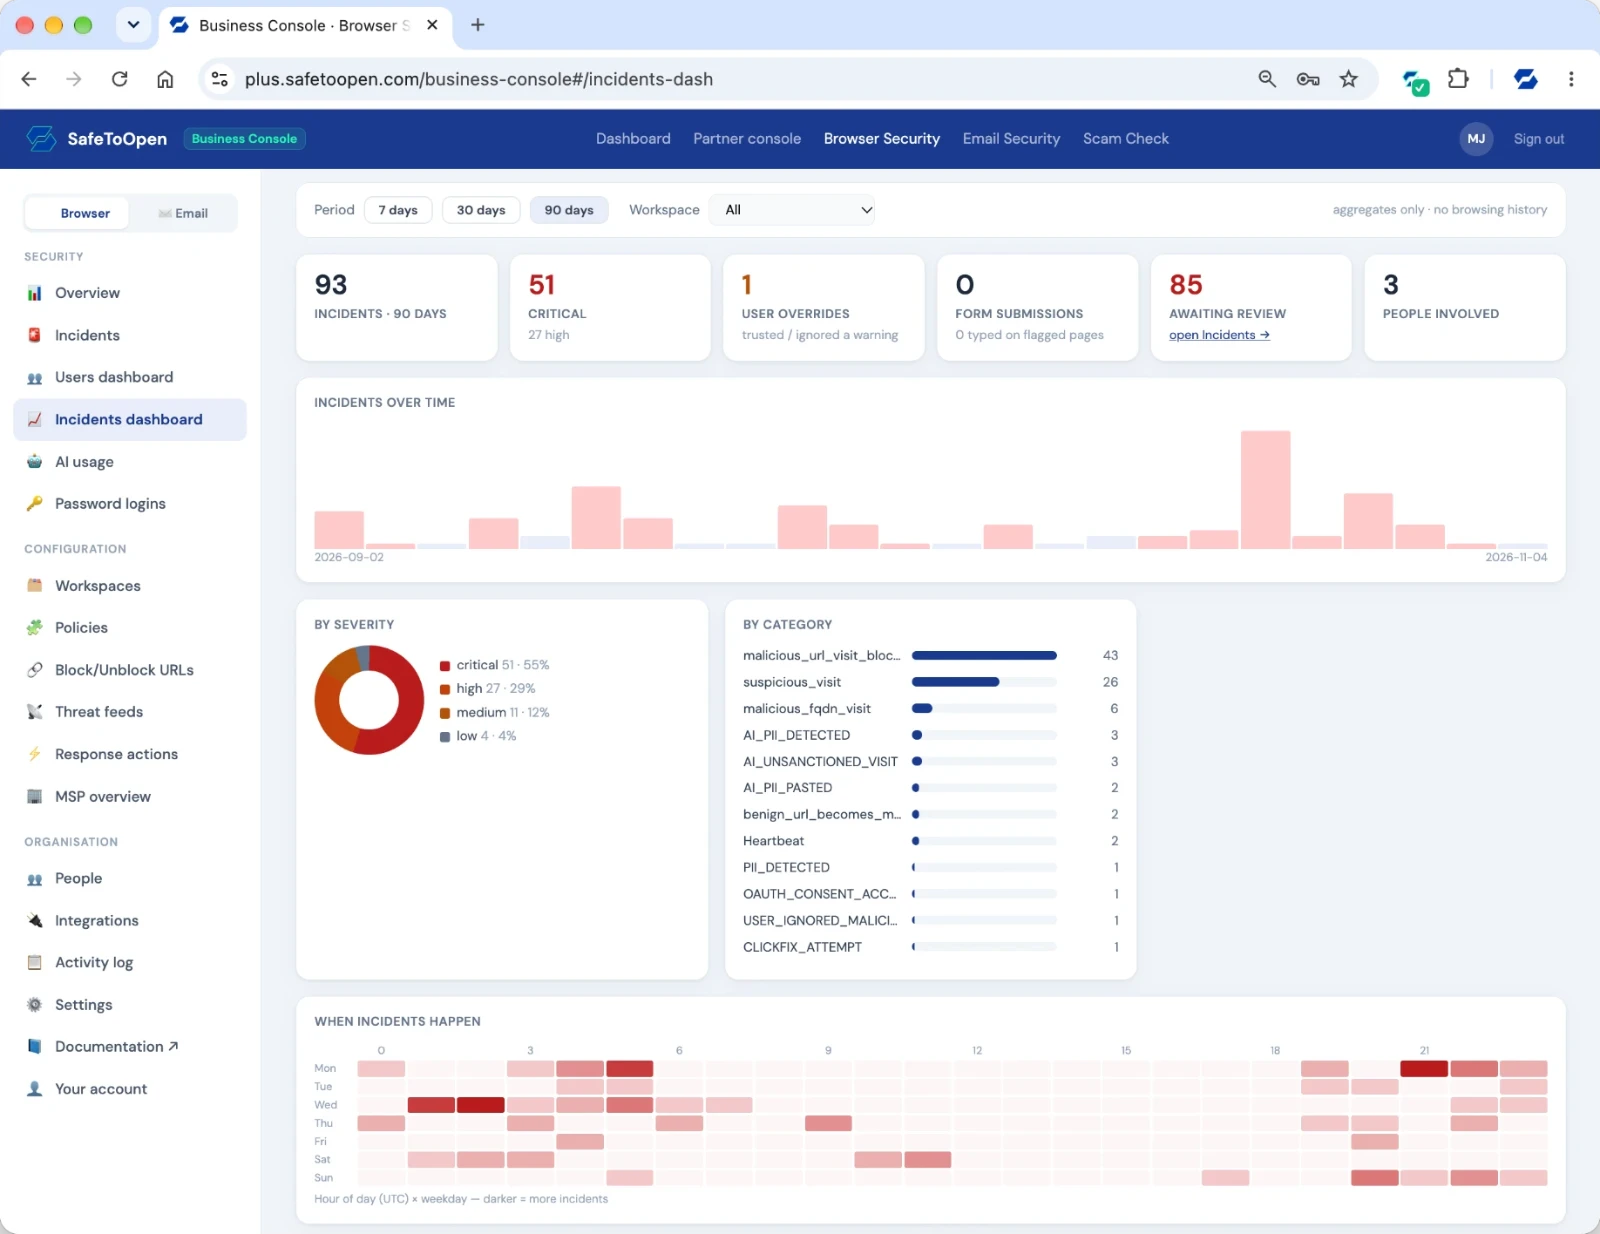
One browser security layer that blocks threats coming in — phishing and malware — and stops sensitive data going out.
Defender, your gateway and your identity provider stay the enforcement points. SafeToOpen adds the verdict they cannot produce on their own, then hands it to them: one confirm in the console, in Slack or in Teams, and every configured action runs at once. Or let rules run on their own above a severity you set.
Which AI tools are in use, how many people use them, and what was warned or blocked.
Shown with test data.
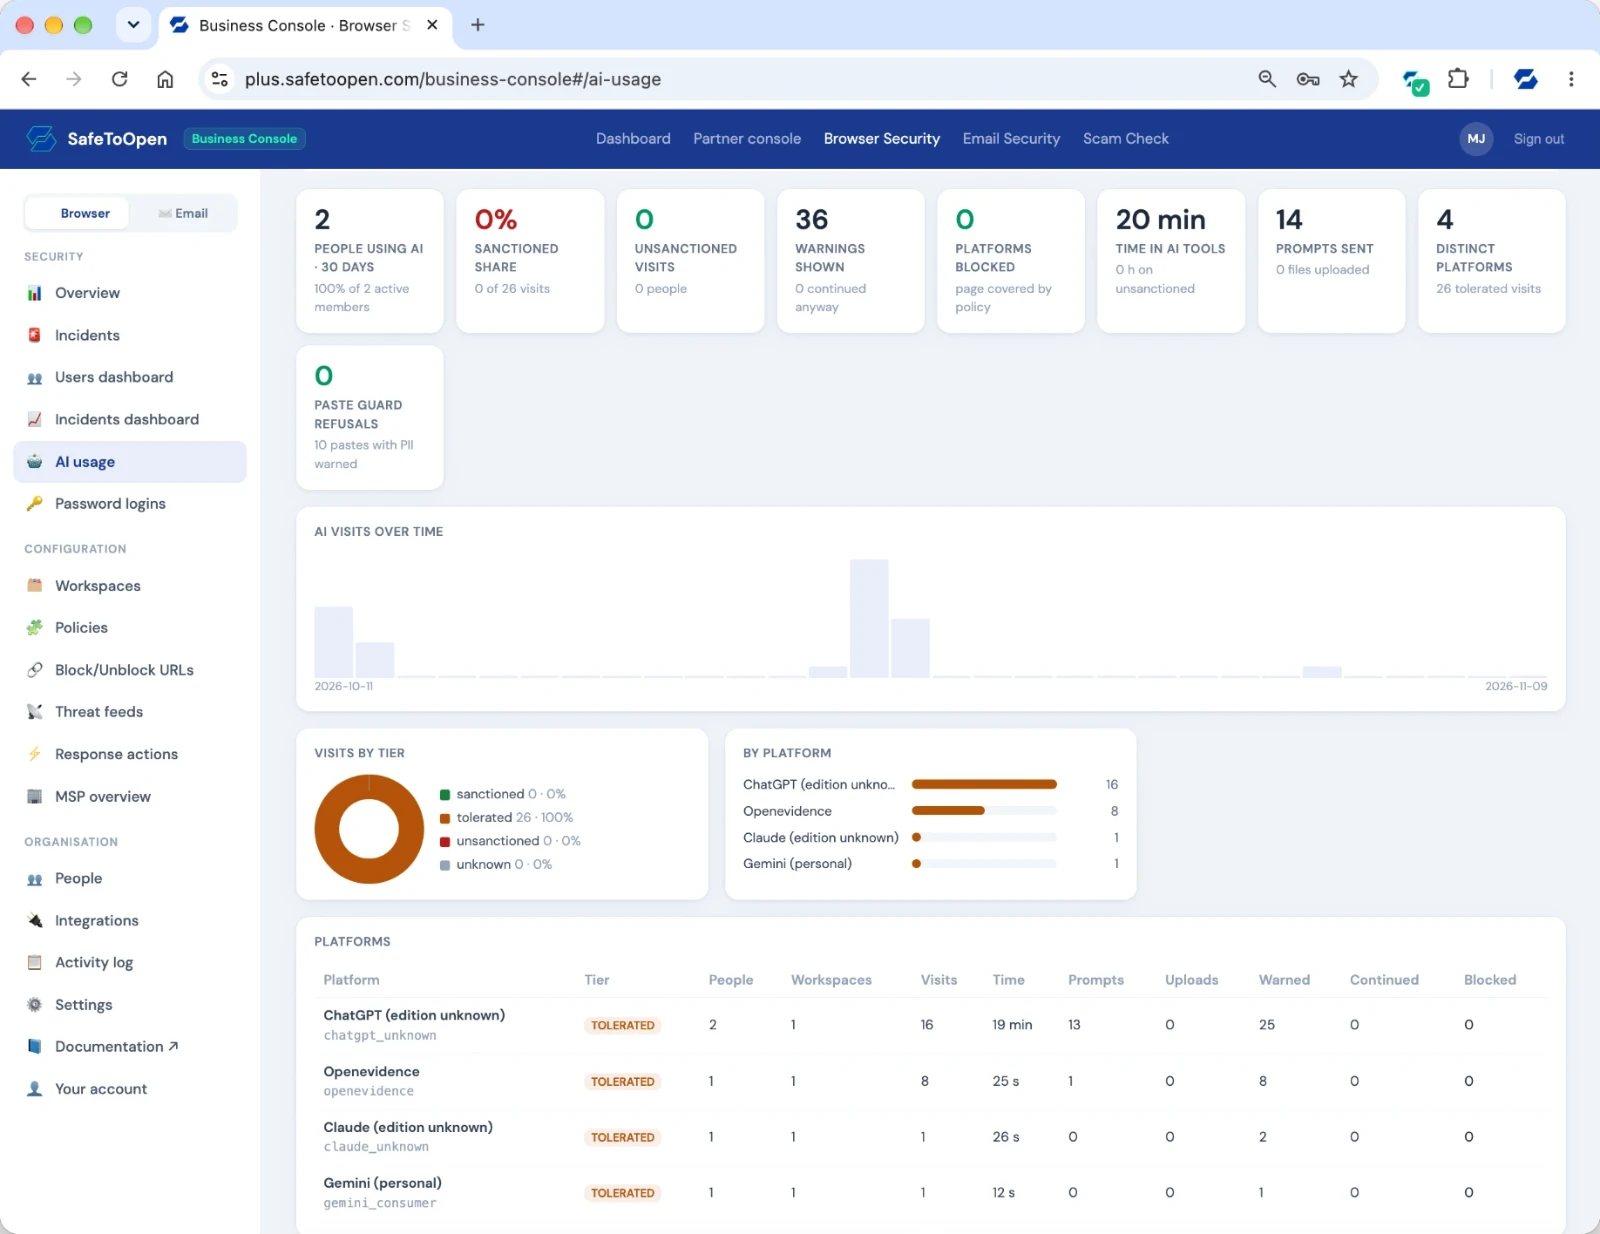
Name the AI platforms you sanction, warn on or block the rest, keep personal and confidential data out of unsanctioned tools at the moment of the paste, and show the board and the auditor who uses which AI.
Phishing pages are no longer the only way in. Browser Security now stops the three attacks that walk past URL filtering and MFA, and keeps an inventory of every app your people sign in to without single sign-on.
Gateways and filters wait for a threat to be known. SafeToOpen judges it the moment it appears, at the point of click.
| Capability | SafeToOpen | Email gateway (Proofpoint, Mimecast) · Defender · web filter |
|---|---|---|
| Catches zero-day phishing | ||
| Protects at the point of click, in-browser | ||
| Verifies email in Outlook & Gmail | Partial | |
| Deeper Analysis for BEC / executives | Partial | |
| No browsing data collected or sold | ||
| SIEM / SOAR integration | Varies | |
| Pushes a confirmed block into your DNS filter, EDR, firewall, mail gateway and IdP | Manual |
Editable PowerPoint briefings for presenting SafeToOpen to leadership, IT and security — with the talk track and sources in the speaker notes, a demo walk-through and a proposed pilot.
Phishing protection at the point of risk: how detection works, what people see, deployment, incident response, privacy and a two-week pilot.
Business email compromise, verification inside Outlook and Gmail, up to 71 checks, plan fit, data handling and a pilot for the people most exposed.
Measuring scam awareness with an open, timed assessment: the evidence, a live exercise, campaign set-up, privacy choices and a first campaign.
Add your organisation’s name on the cover and present. A managed service provider? Get the client presentations →
We'll show real-time, zero-day detection on live examples, walk through central management, and map SafeToOpen to your environment.
Through a central management console. Admins roll out the browser extension and email security across the organization, assign Plus or Executive seats per person, set policies, and view reporting.
Yes, in both directions. Detections flow out to your SIEM (JSON, OCSF, ECS or CEF), to ServiceNow and Jira, and as STIX/TAXII threat intelligence. Confirmed incidents flow into your enforcement points as response actions: Cisco Umbrella, Zscaler, Netskope, Cloudflare Zero Trust, Microsoft Defender for Endpoint, CrowdStrike, SentinelOne, Sophos, Trend Vision One, Microsoft 365, Mimecast, Proofpoint TRAP, Harmony Email, Cisco ETD, Barracuda, FortiMail, Entra ID, Okta, Google Workspace, Slack, Teams, PagerDuty, Opsgenie and a hosted blocklist for firewalls. Your own threat feeds are ingested and blocked in every browser. See Integrations & automated response.
Yes. Executive seats add Deeper Analysis for targeted and business email compromise attacks, sender and writing-style verification, and impersonation alerts. Business Plus lets you mix Plus and Executive seats in one organization.
SafeToOpen is privacy-first and GDPR-ready, with no collection or sale of browsing data, which suits government and regulated environments. Contact us to discuss specific compliance requirements.
Yes. Each AI platform edition is sanctioned, tolerated or unsanctioned per workspace; the extension tells the work edition of ChatGPT, Gemini and Claude from a personal account, shows your message or blocks, and Paste Guard refuses pastes, prompts and uploads carrying personal information on unsanctioned tools. Microsoft and Google tenant restrictions can be enforced from the extension too. The AI usage report gives ISO 42001 and EU AI Act evidence in one export. See Shadow AI governance.
Yes, all three are workspace policies in Browser Security. The ClickFix guard replaces a command a page copies to the clipboard and records the payload as a critical incident. The OAuth consent guard reads Microsoft and Google consent screens and warns on or blocks apps outside your approved list that ask for mailbox, files, contacts or offline access. Password Alert fingerprints the work password on your identity provider and catches it being typed anywhere else, including proxy phishing kits that defeat MFA. A Password logins report lists every site people sign in to without single sign-on. See the guards.