
Would your people spot a real scam? Now you can know.
Scam Check is a security awareness test for employees: a timed, branded scam-spotting test built from the techniques criminals actually used between 2024 and 2026 — lookalike domains, fake CAPTCHAs, payment redirects, deepfake calls — across email, text, phone, QR and six more channels. Every person gets their own link and their own questions. You get a score, not a guess.
Even careful people miss a few
That is not a failing — it is how good the scams have got. Anyone can take our free public quiz, twelve questions built from the same material Scam Check uses, and here is how everyone has done so far. It updates as new results come in.
We test judgment, openly
No traps, no fake emails from “HR”. People know they’re being tested — then they meet the real techniques, under time pressure, and every answer is scored. Try a real question, and find every red flag:
Build it. Send it. Read it.
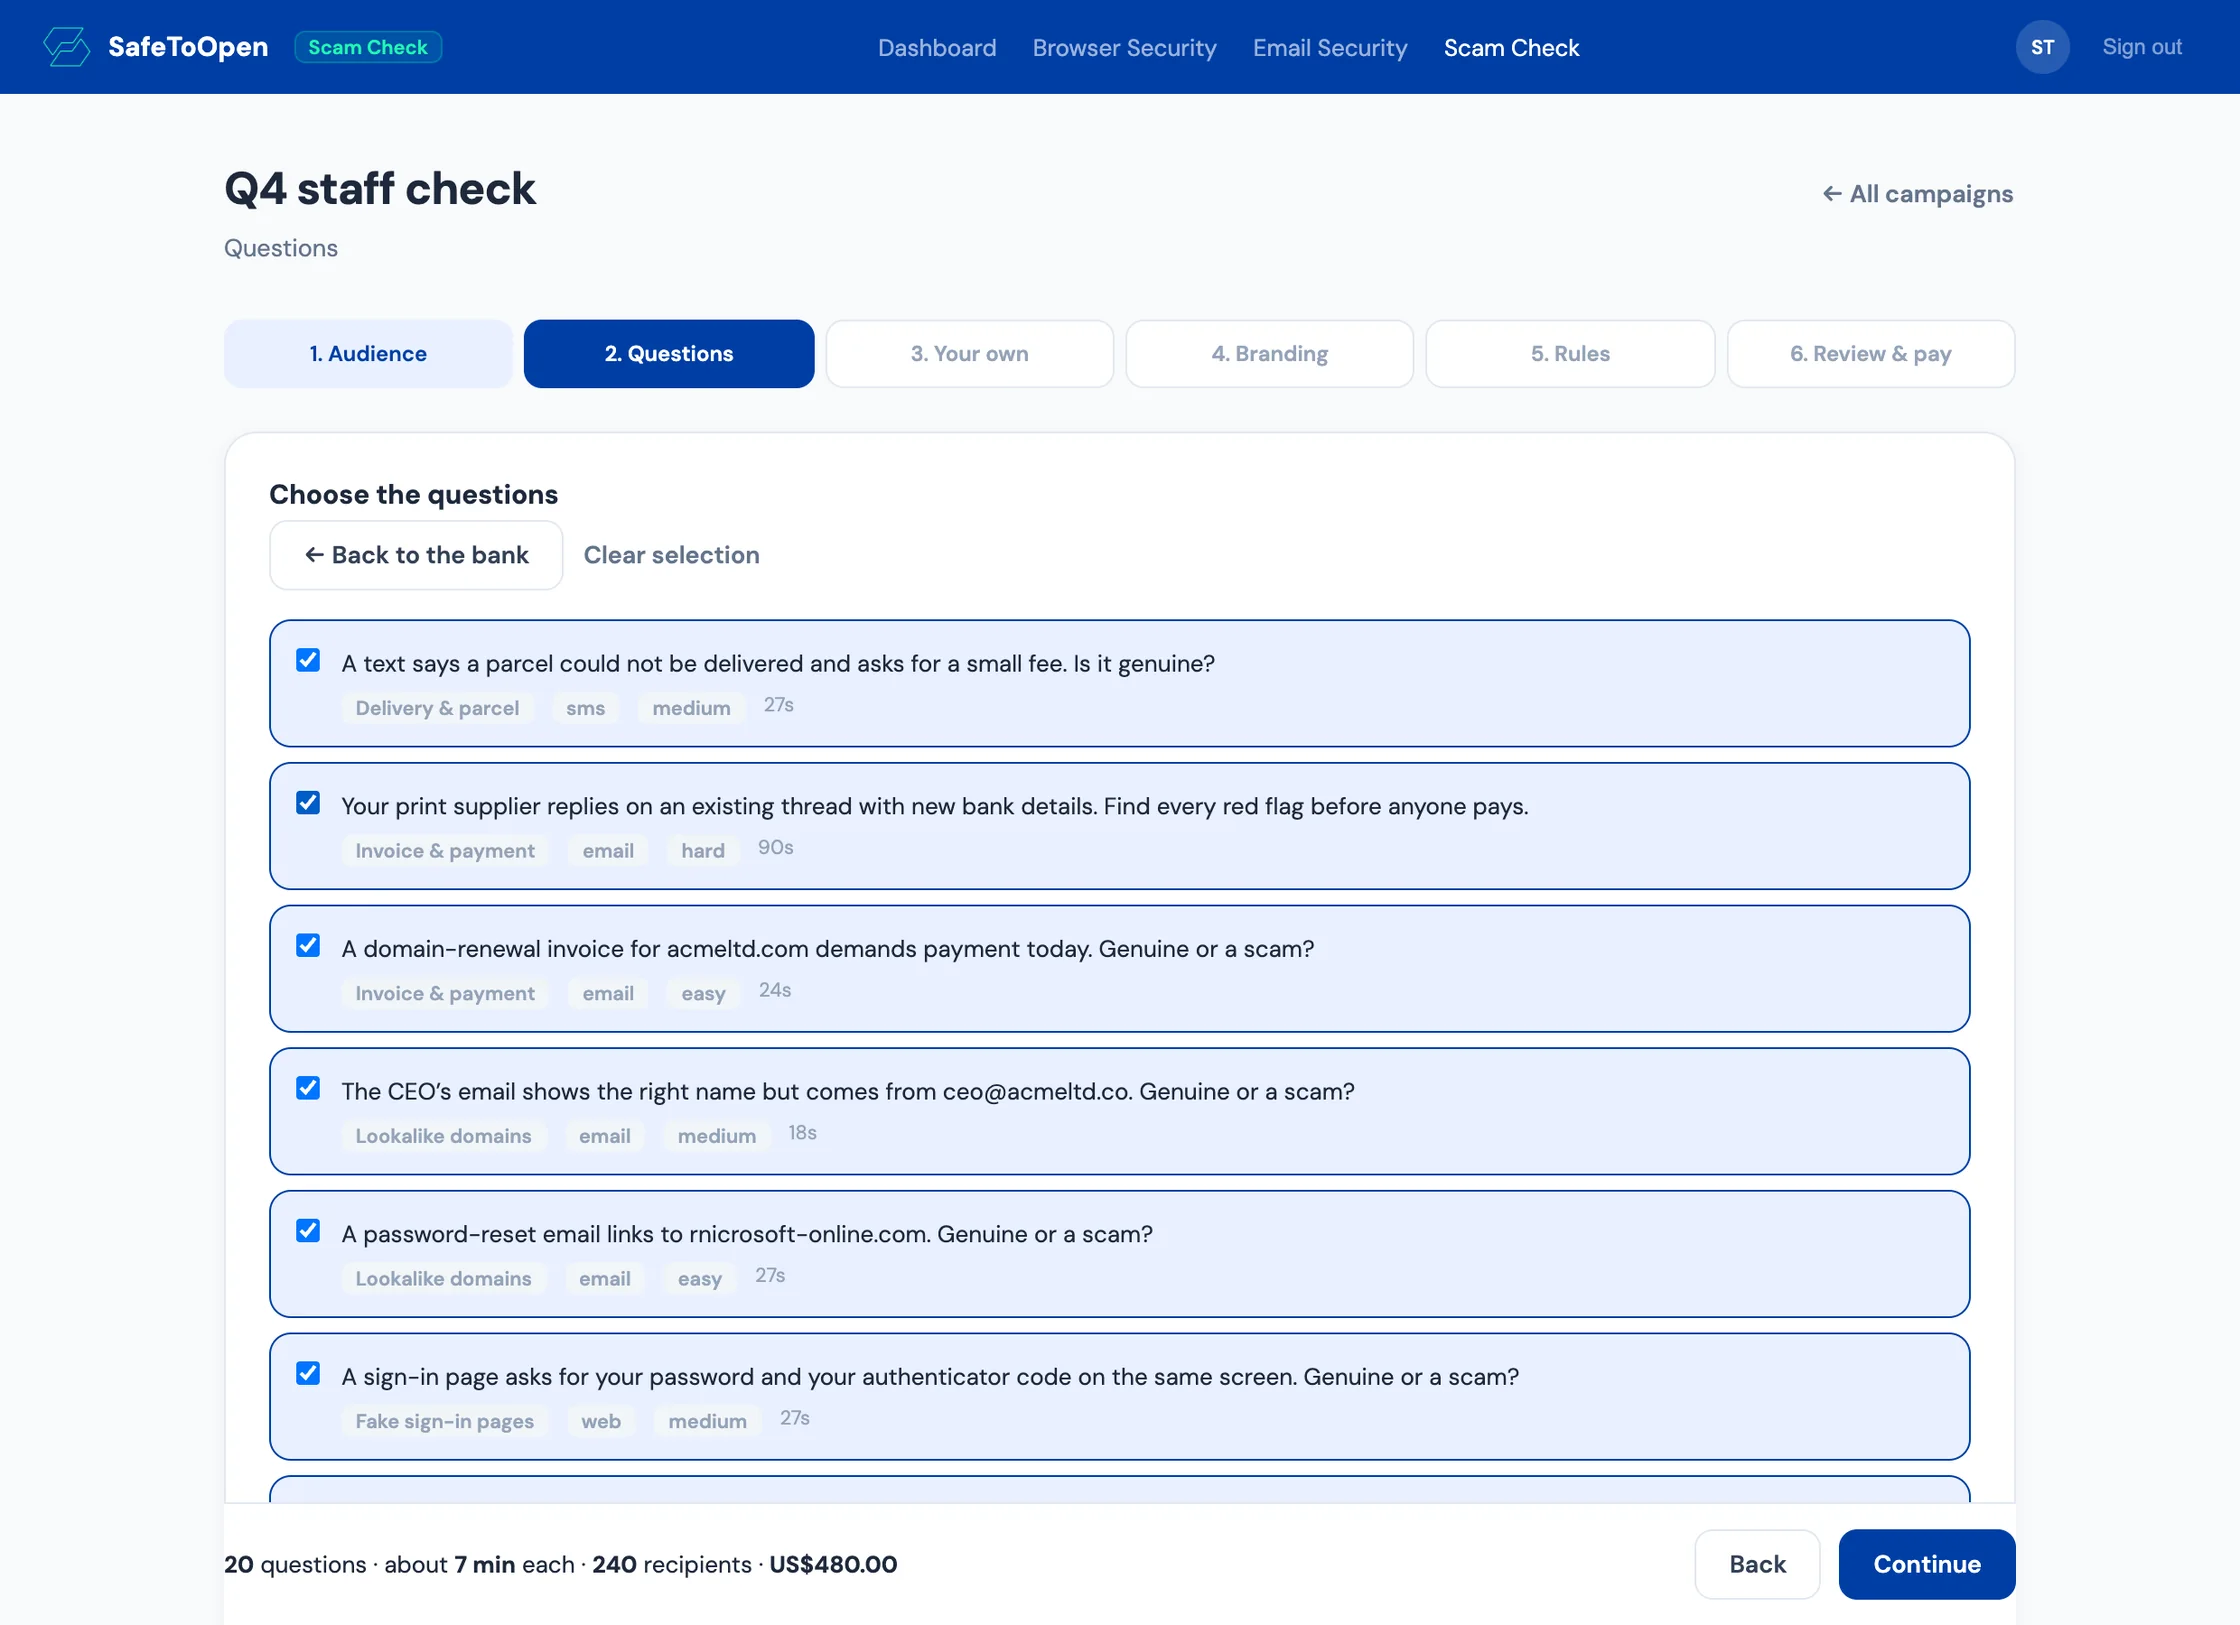
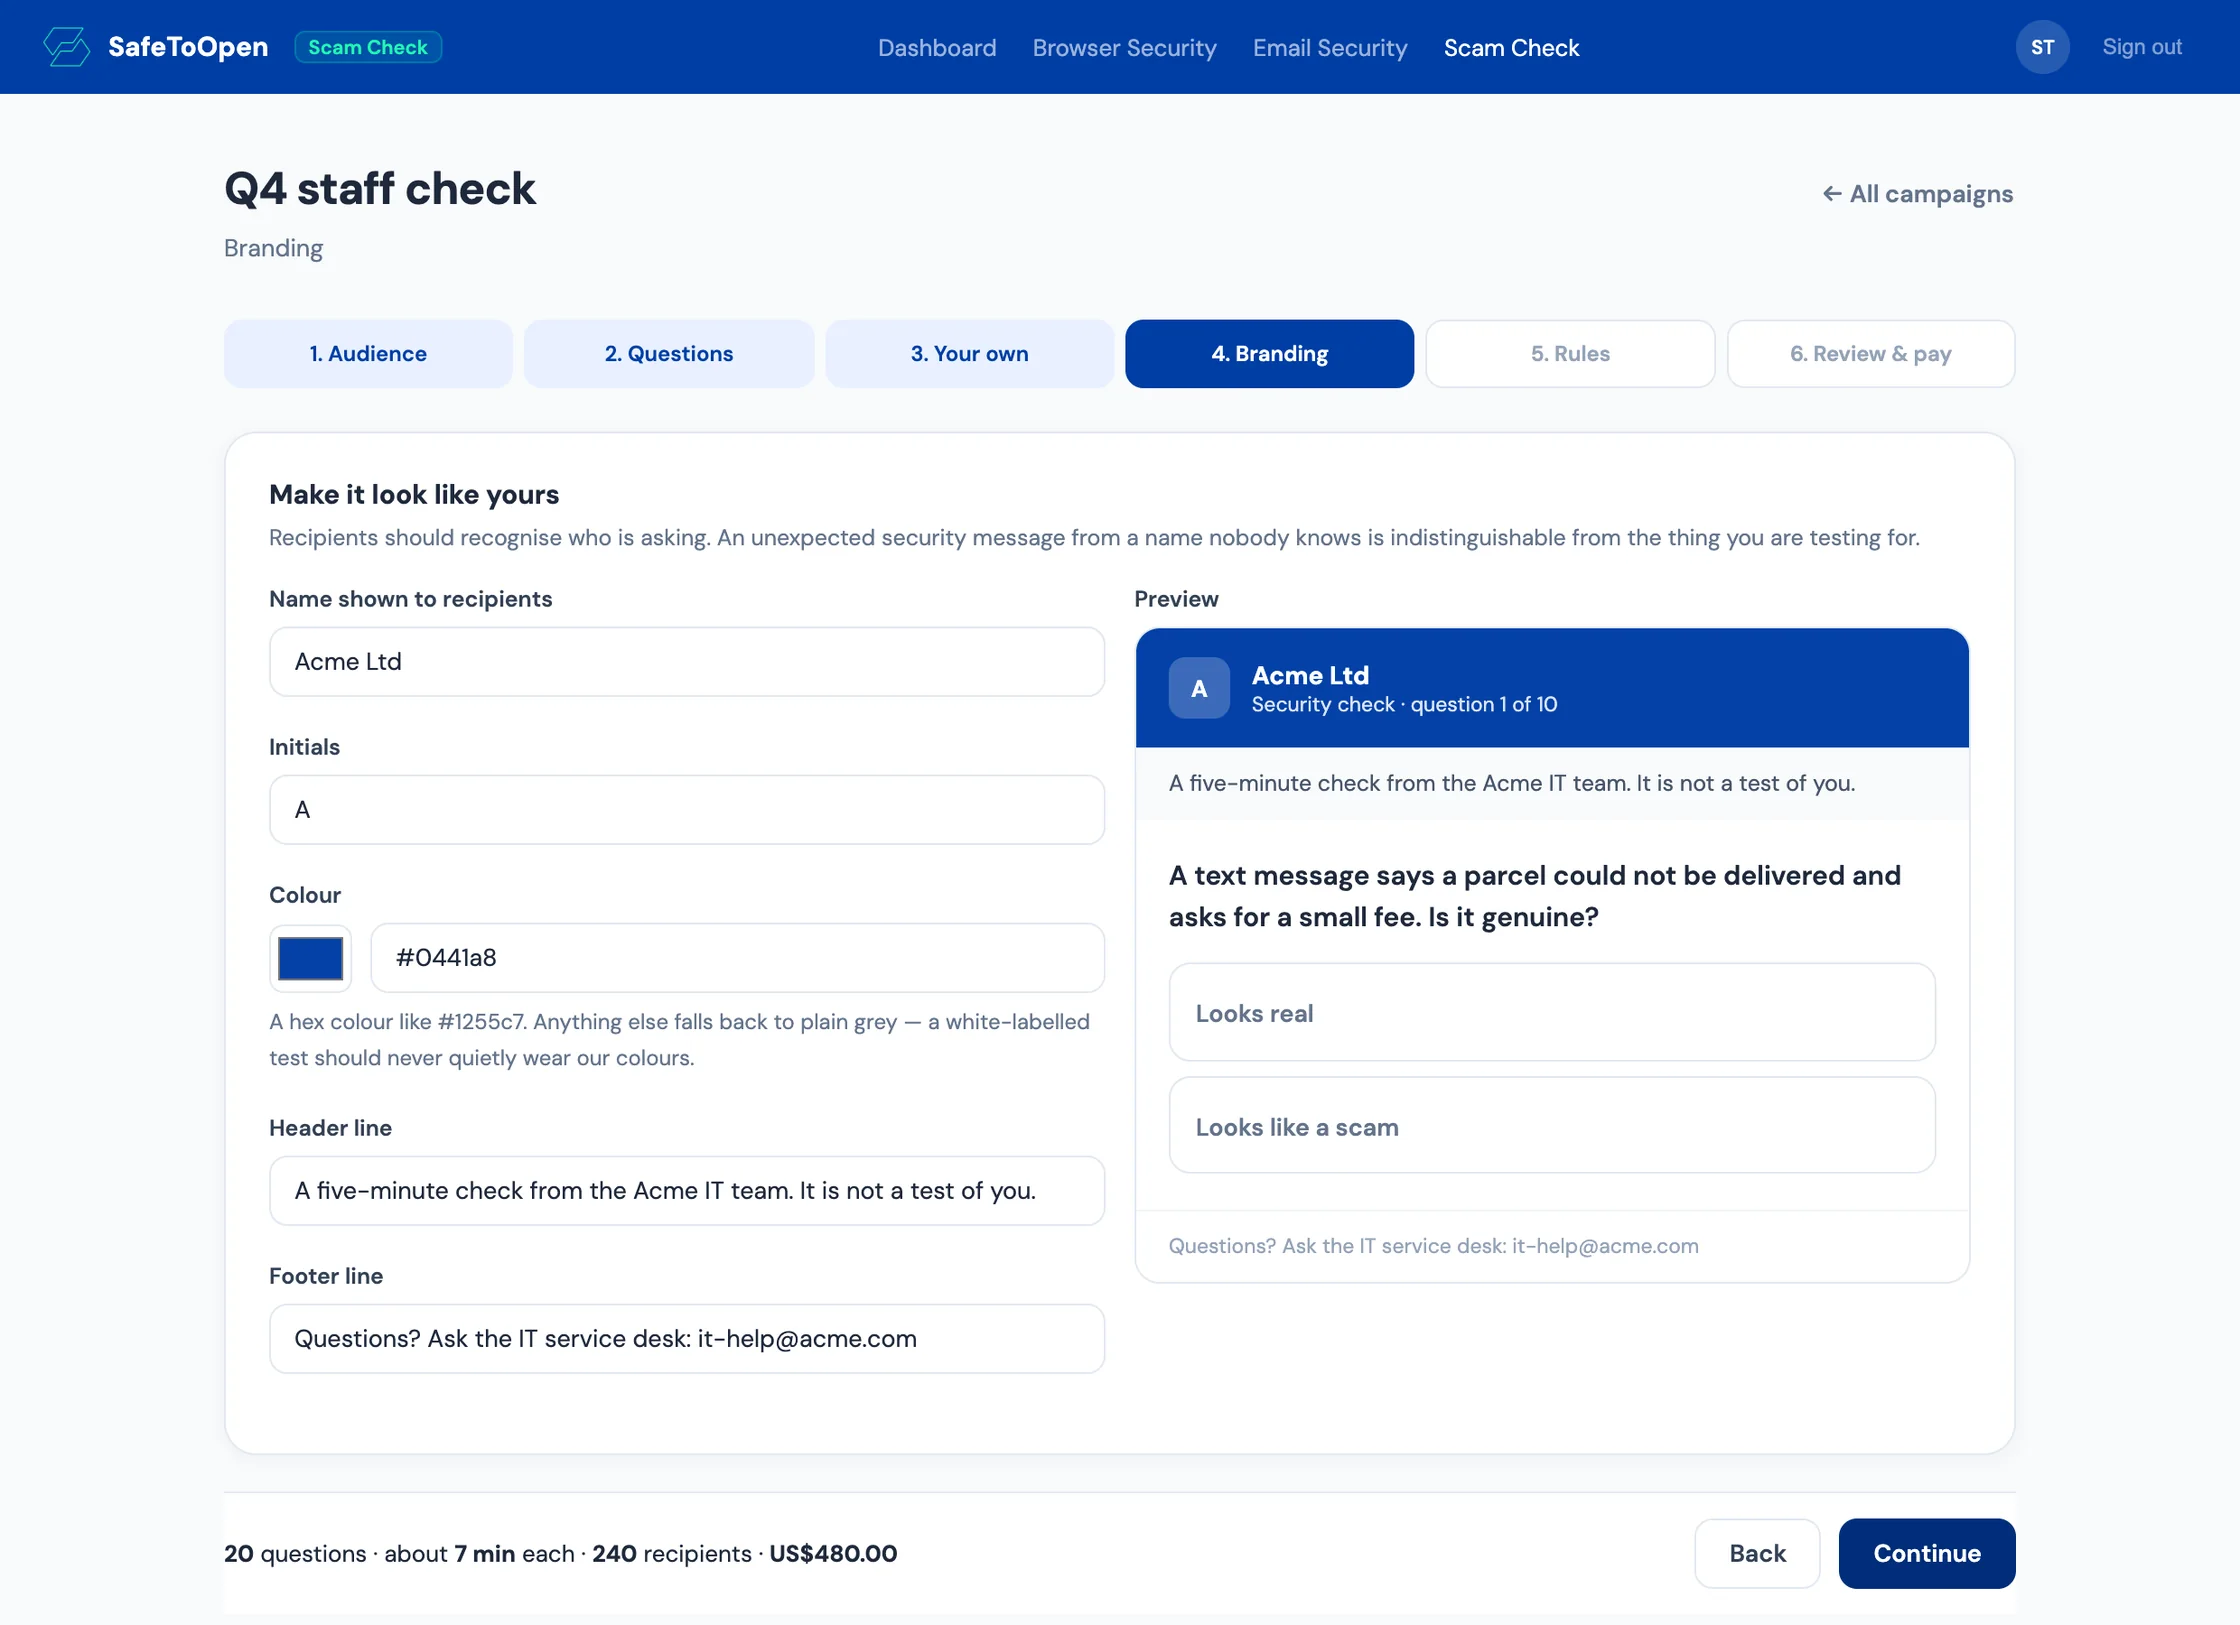
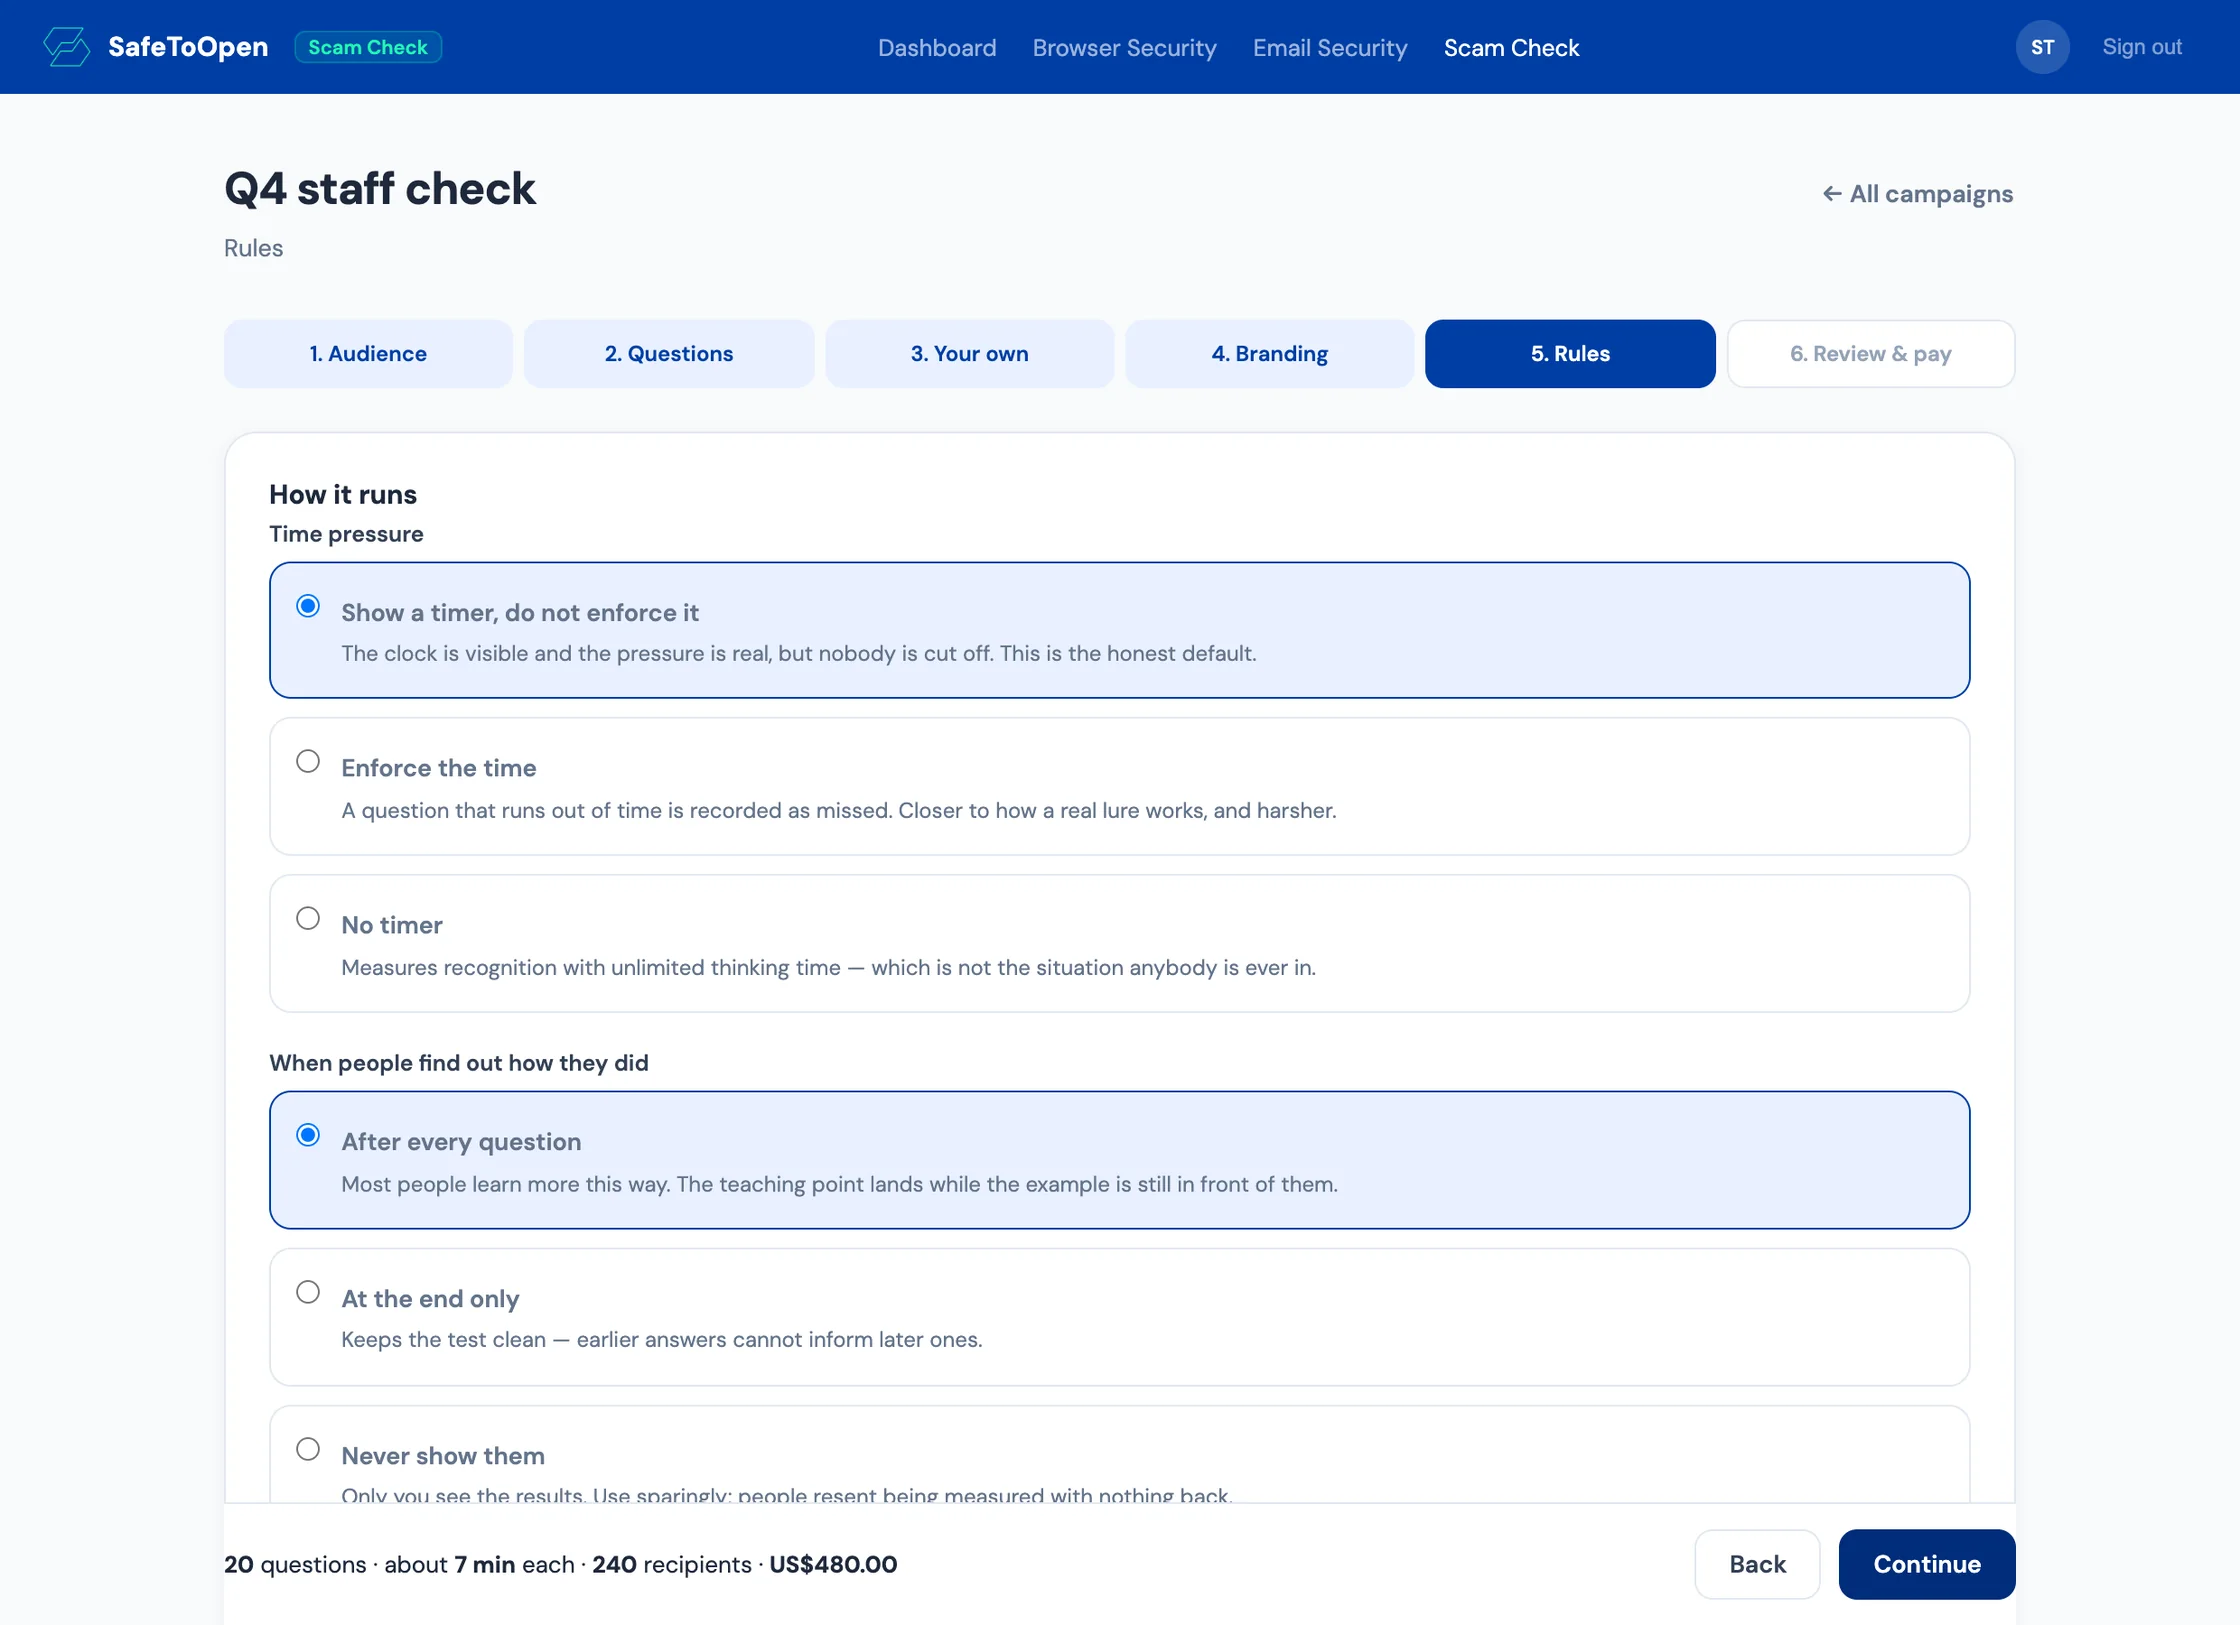
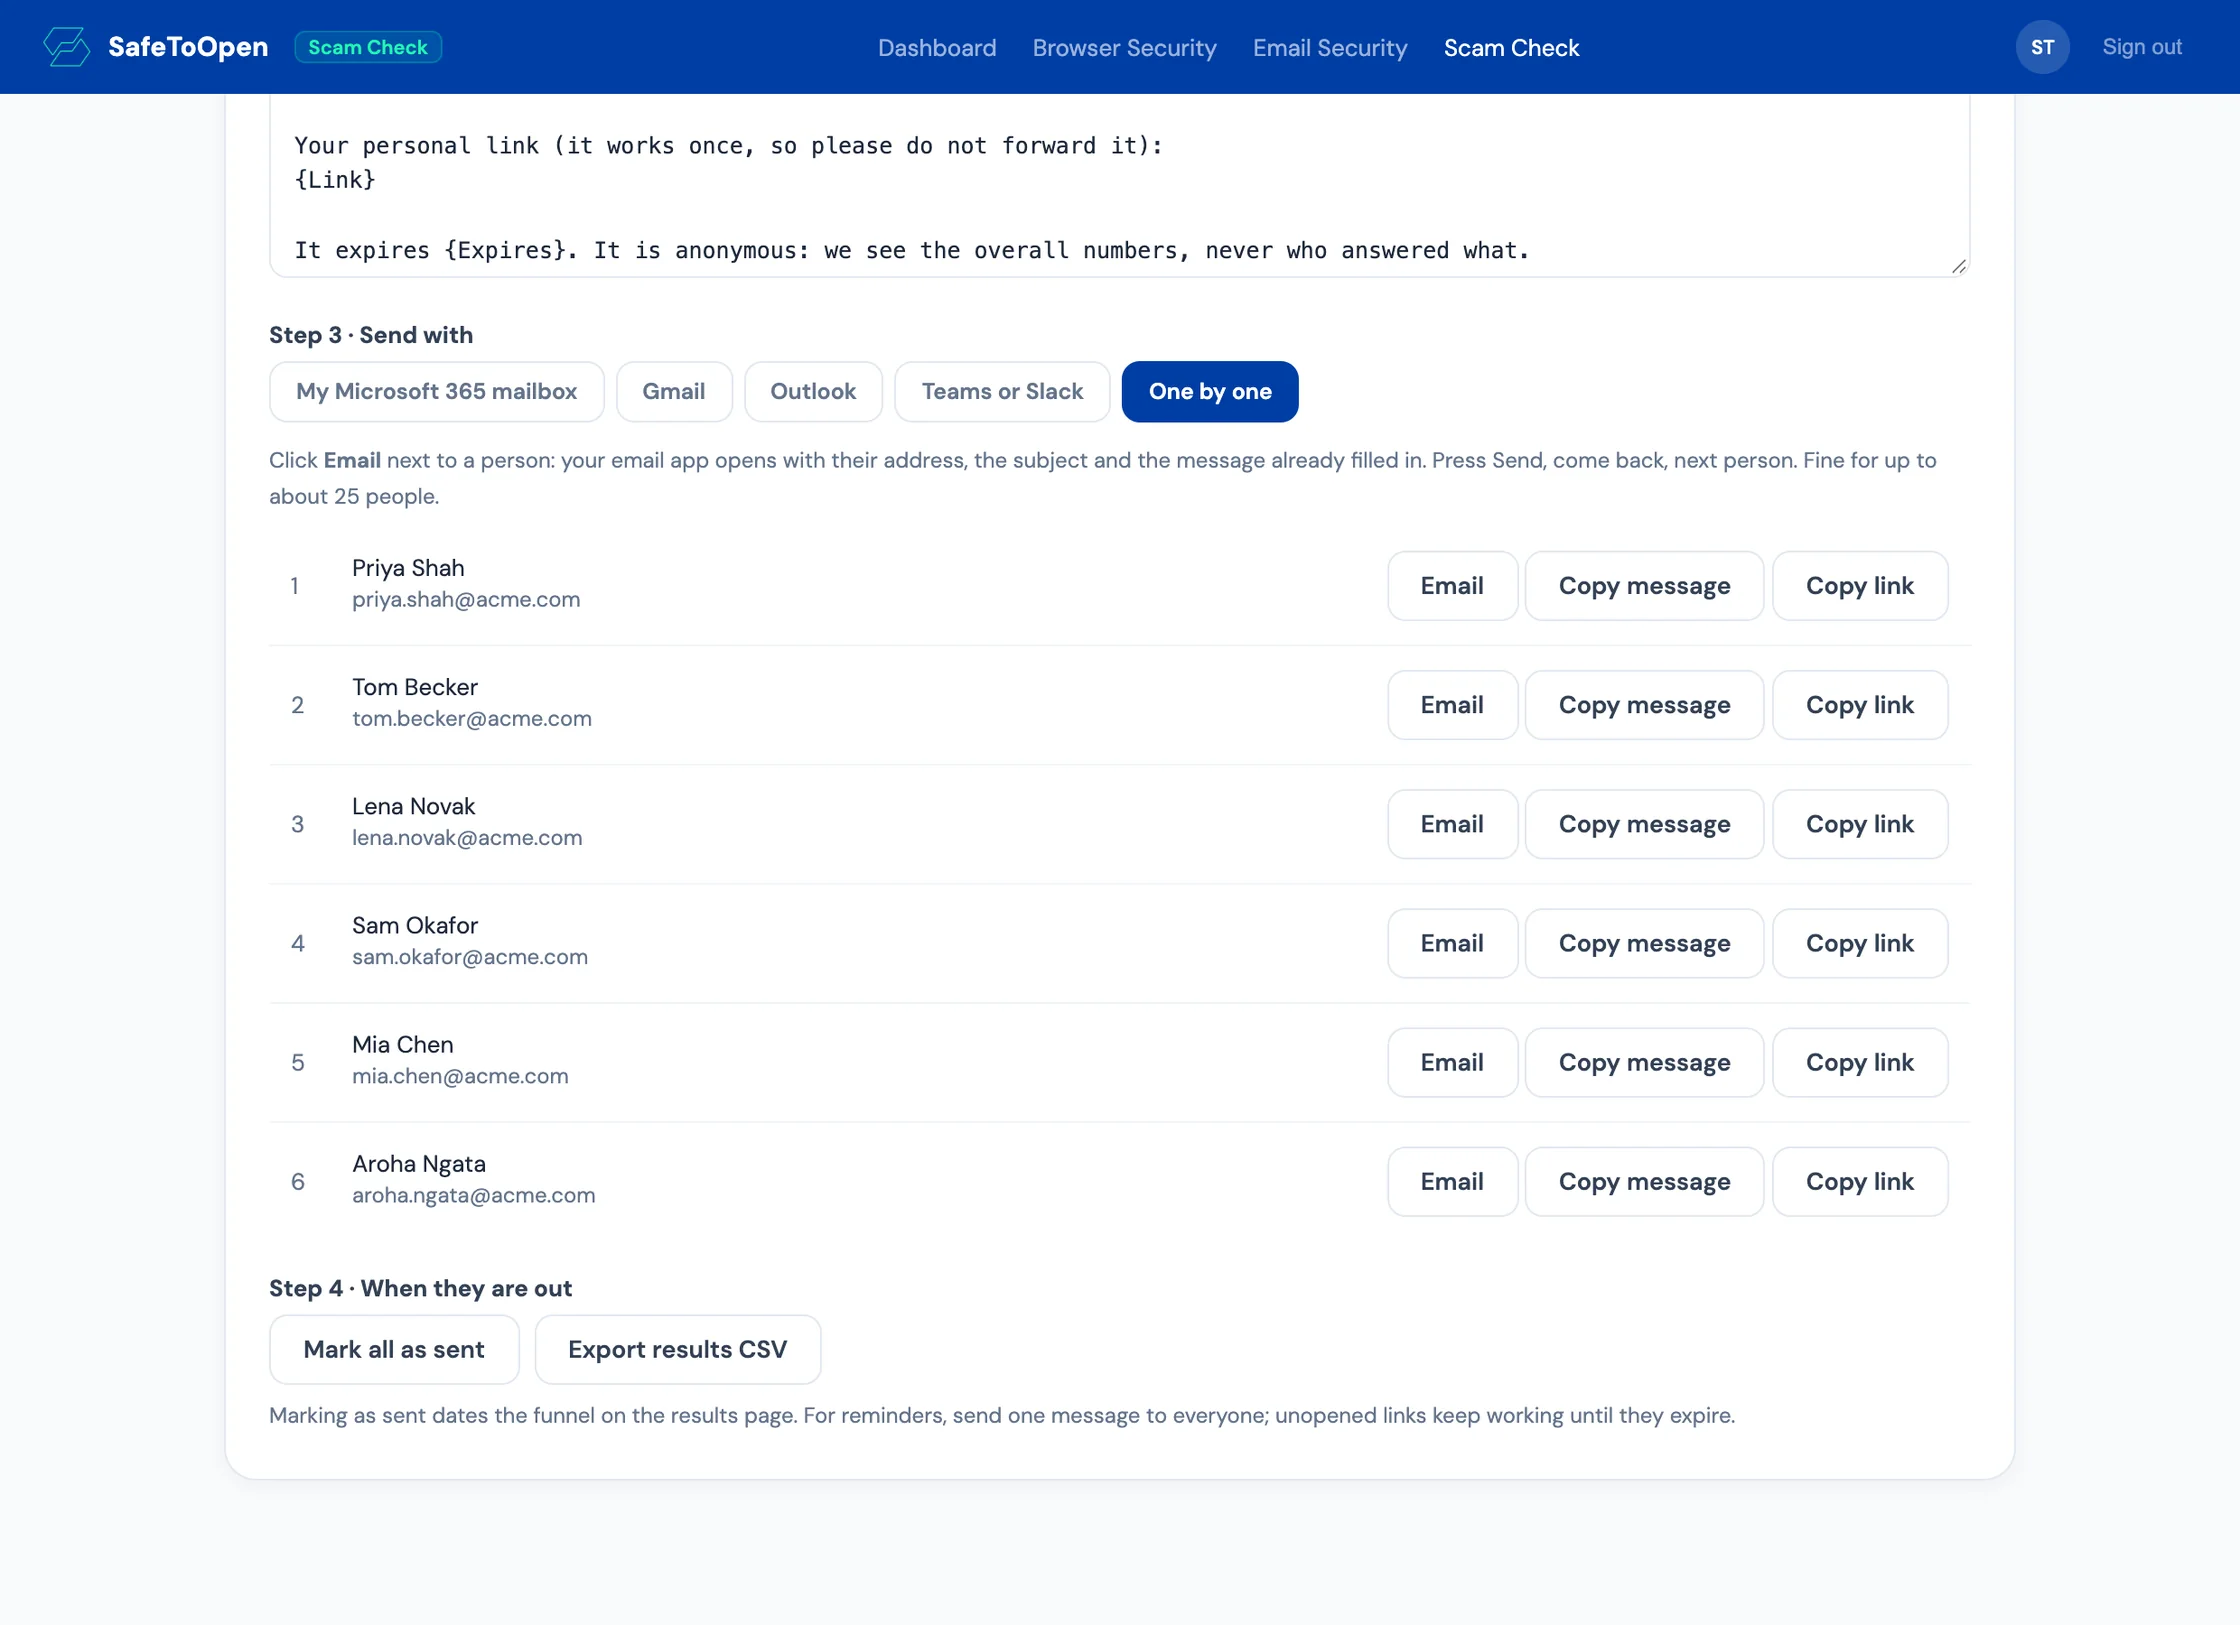
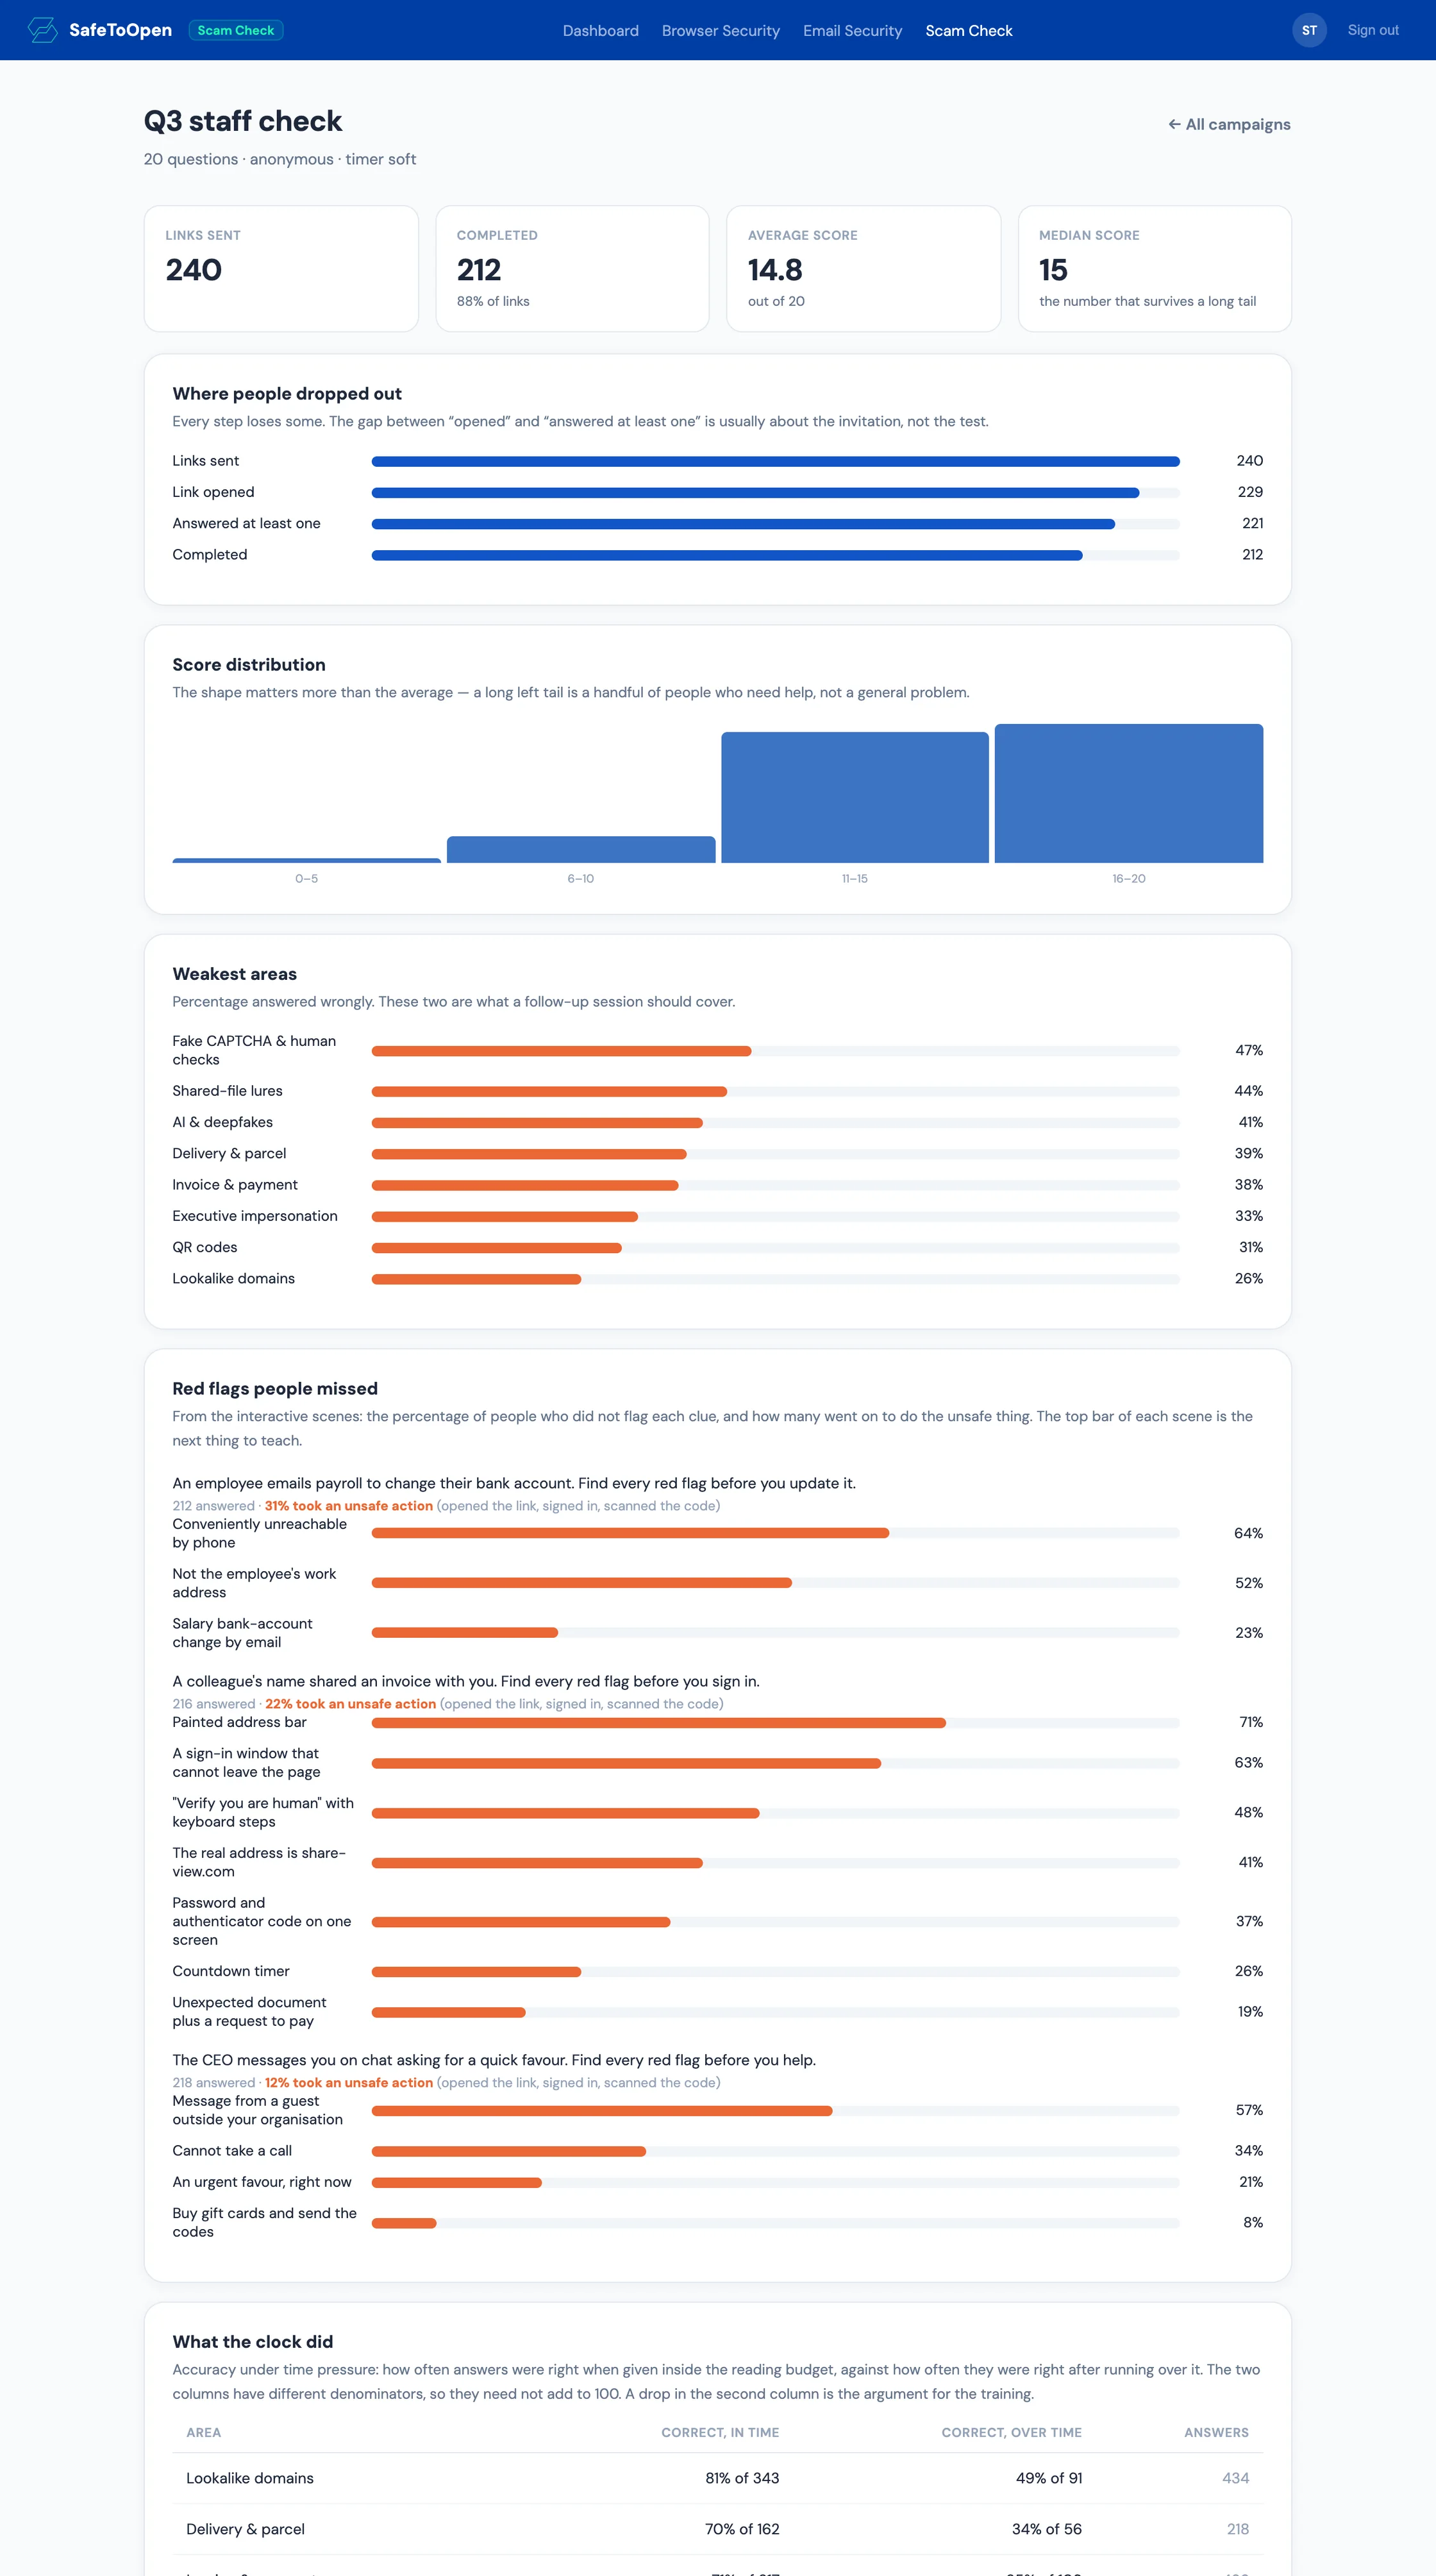
The real Scam Check console, with example data.
243 questions, across every way a scam actually arrives
All of it written from real scam techniques seen between 2024 and 2026 — not a template library that has been sitting still since someone wrote it. Pick a whole category, filter to the channels your people actually use, or let the builder spread a campaign across all of them.
The bank is refreshed monthly from what our scanner sees in the wild, so a question tagged seen this month is a lure that was live against real people weeks ago. That is the part a static training library cannot copy.
Scam Check vs a phishing simulation, side by side
What a fake-phishing-email campaign tells you, against what a Scam Check tells you.
Eight differences that matter
| A commonly-used phishing email campaign | SafeToOpen Scam Check | |
|---|---|---|
| What’s measured | ✗Who clicked one template email | ✓Scored judgment across real scam techniques |
| Non-participation | ✗Counted as a pass — silence looks like skill | ✓Visible as “not started” — you know who you know nothing about |
| Channels tested | ✗Email only | ✓Email, SMS, voice, QR, web, chat, social, app, marketplace, post |
| Realism | ✗Template library | ✓Lookalike domains, fake CAPTCHAs, payment redirects, deepfakes, regional scams |
| Staff experience | ✗Deception — documented trust and HR fallout | ✓An open test people can even enjoy — feedback after every answer |
| Who you can test | ✗Employees on your directory | ✓Staff and customers — white-label, no directory needed |
| Privacy | ✗Per-employee tracking, always | ✓Anonymous mode: results without names ever stored |
| Pricing | ✗Per-user annual subscription | ✓Pay per campaign. Run one, or four a year — your call |
Read the full comparison: phishing simulation vs security awareness test → · how to run a phishing test for employees →
Run the first one free. Then pay once per campaign.
Try it on a department before you spend anything. After that you pay once, for the number of people you are testing — not per seat, not per year, and not again next month. A 100-person company runs its annual scam check for US$200.
Then, for the whole organisation:
Part of Business Plus. Testing a customer base of 10,000 or more? Talk to us about population pricing.
Questions we get
A security awareness test measures how well people recognise real scams and phishing, instead of teaching or tricking them. Scam Check is one: a short, timed test built from real scam techniques across email, text, phone, QR and more, scored per person and per team, so you know who would be caught out before an attacker finds out.
No — deliberately. Nobody is tricked and nothing is disguised. People take an open, timed test against real scam techniques, get feedback after every answer, and are scored on judgment. You get better data, and your staff don’t learn to resent security.
Never. You get one personal link per person and send them yourself, from your own address — so the invitation arrives with your name on it, and your sending reputation stays yours. An unexpected email from an unknown security vendor asking people to click a link would be exactly the thing we’re testing for. Sending is quick: the console pairs each link with a person, gives you a mail-merge file, and walks you through Gmail, Outlook, Teams, Slack or one-by-one sending in about five minutes. Read the sending guide →
Yes. In anonymous mode no address is ever written to our database — not hidden, not hashed, never stored. You see the scores and the gaps; nobody sees names. It’s the mode works councils and privacy teams approve.
Yes — it’s built for it. The test is fully white-label, needs no directory or login, and includes country-specific scam content. If your organisation carries the cost when customers are scammed, measuring their scam literacy is the first step to reducing it.
Completion and score records export per campaign, which is the evidence ISO 27001, SOC 2 and PCI DSS awareness controls — and cyber-insurance questionnaires — ask for. A scored assessment is stronger evidence than a completion certificate, because it shows what people can actually do.
Run your first campaign this week
Build it in an afternoon, send it from your own address, and know by Friday where the gaps are.